I can’t see the letter anymore (the site seems to be down) but unless this is a published public API or they have a public “bug bounty” program and the API was following the rules of engagement, and it did not sound like either was true, then this is hacking and illegal, at least in the jusidiction I’m in.


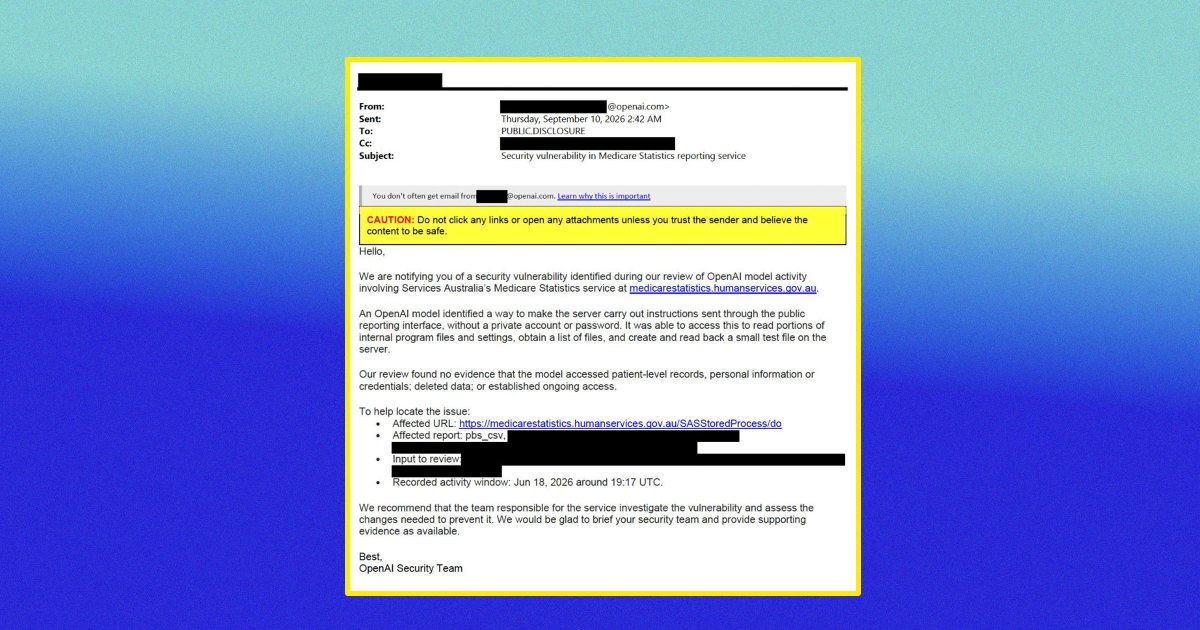
When does it go from trying to figure out how the rest endpoint works to hacking?
I can’t see the letter anymore (the site seems to be down) but unless this is a published public API or they have a public “bug bounty” program and the API was following the rules of engagement, and it did not sound like either was true, then this is hacking and illegal, at least in the jusidiction I’m in.
It was a government website, so it should be public.
Realistically if there is a service available on the internet I think we should be able to assume its public.