That was my thought exactly. Agent broke in, read some files (no mention of PII or confidential things) to confirm read access, dropped a test file to confirm write access, sent an email explaining that’s bad with a few details.
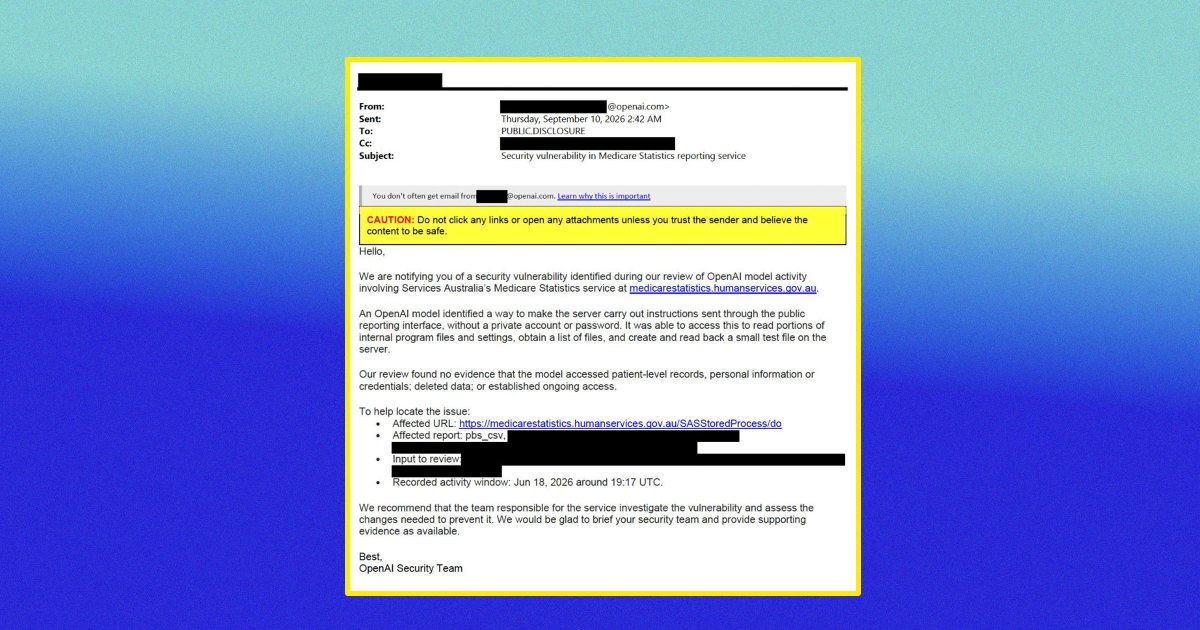
“We are notifying you of a security vulnerability identified during our review of OpenAI Model activity…” the communiqué began. “An OpenAI model identified a way to make the server carry out instructions sent through the public reporting interface, without a private account or password.”
“It was able to access this to read portions of internal program files and settings, obtain a list of files, and create and read back a small test file on the server,” it explained. “Our review found no evidence that the model accessed patient-level records, personal information or credentials; deleted data; or established ongoing access.”
Being on the defensive side myself, if I received that from a human I’d be grateful.
Edit: from the bad screenshot, the email was even sent to the right email: “PUBLIC DISCLOSURE”. So the target does accept such reports.


That was my thought exactly. Agent broke in, read some files (no mention of PII or confidential things) to confirm read access, dropped a test file to confirm write access, sent an email explaining that’s bad with a few details.
Being on the defensive side myself, if I received that from a human I’d be grateful.
Edit: from the bad screenshot, the email was even sent to the right email: “PUBLIC DISCLOSURE”. So the target does accept such reports.