Morally clear? grey. If their ‘hacking’ accidentally causes issues with the system or it goes down, it’s definitely bad. Whatever was on that system is now in the hands of OpenAI, not great. Because OpenAI is open about it, a lot of people who are even less reputable will do it.
Historically, Pentesting had unwritten rules of engagement. None of that is being followed.
We don’t seem to apply law to AI, that’s a real problem.


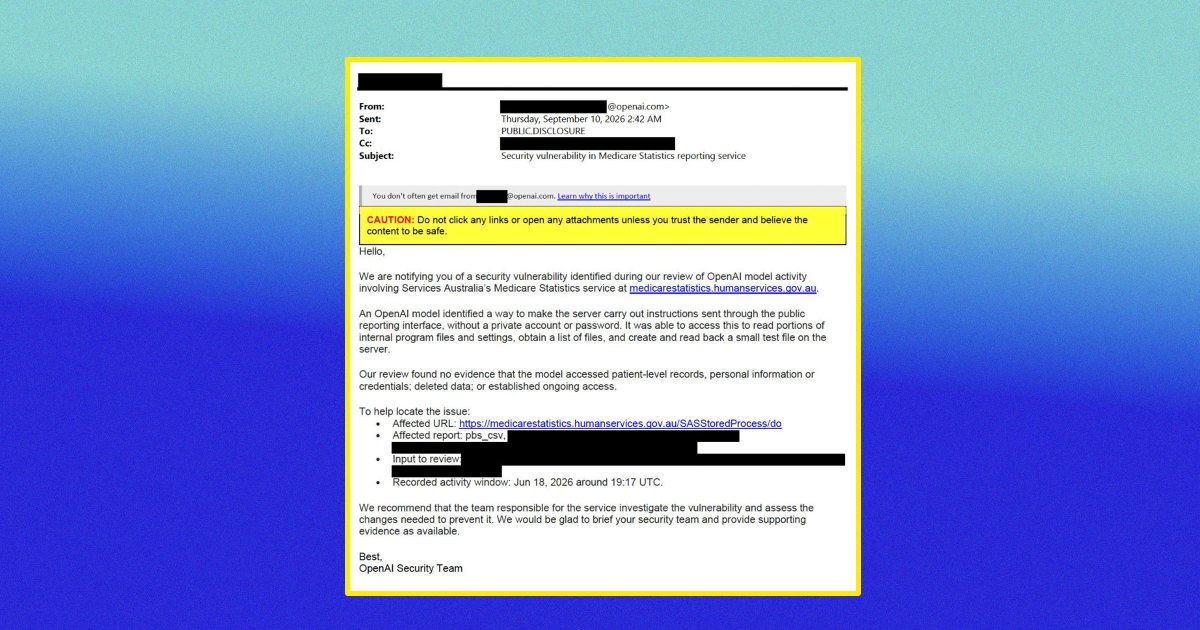
Best for the company? probably.
Morally clear? grey. If their ‘hacking’ accidentally causes issues with the system or it goes down, it’s definitely bad. Whatever was on that system is now in the hands of OpenAI, not great. Because OpenAI is open about it, a lot of people who are even less reputable will do it.
Historically, Pentesting had unwritten rules of engagement. None of that is being followed.
We don’t seem to apply law to AI, that’s a real problem.
But still, best for the company/entity, yeah.