What good will onboard encryption be if the device is seized? They will just figure out how to decrypt.
I guess you’d need to set up asynchronous encrypt / decrypt keys, then move the data encrypted end to end. The target device can do the decrypting, while the bug only does encrypting.
If you ever intend to decrypt the data, don’t you need a decryption key?
I think my point stands, you’d need this device to be only capable of encryption. Otherwise, anyone with access to the device can decrypt it. So it goes without saying, you’d have to push the data to a second device which handles decryption.
Obviously not. Do you store your false equivalency fallacies on the internet in clear text? Apparently so, but I won’t call you stupid for it.
How do passwords get stored? Encrypted.
How do they get read? Decrypted.
What performs the encryption? Keys.
What can the keys be derived from? Passwords.
Where are those keys stored? On the damned device.
Are you telling me, fuck all to the popular mantra that: if they have physical access to device, you’re boned?
State sponsored forensic programs bypass TPM and shit all the time, requiring physical access.
So where is your hypothetical security coming from? To me, it sounds like you’re needlessly giving me a hard time on a subject I probably understand better than you.


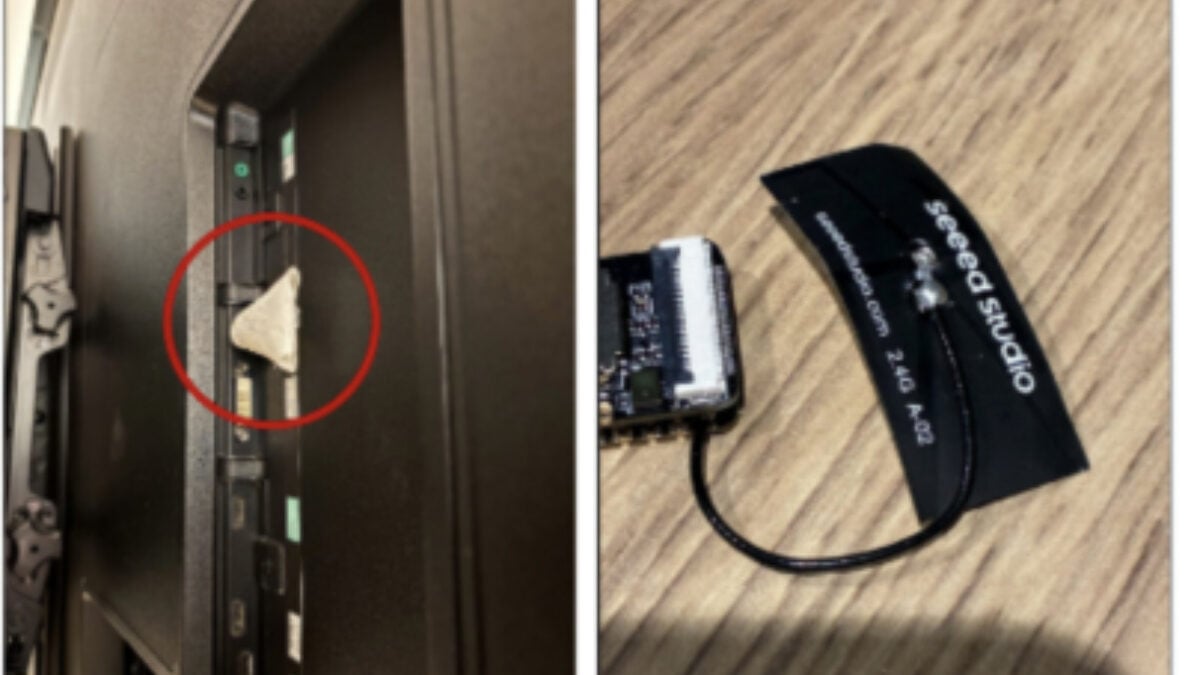
Openais products must be shit at coding if it unsuccessfully encrypted the sdcard as asked to
What good will onboard encryption be if the device is seized? They will just figure out how to decrypt.
I guess you’d need to set up asynchronous encrypt / decrypt keys, then move the data encrypted end to end. The target device can do the decrypting, while the bug only does encrypting.
Thats not how encryption works when implemented properly
How so?
If you ever intend to decrypt the data, don’t you need a decryption key?
I think my point stands, you’d need this device to be only capable of encryption. Otherwise, anyone with access to the device can decrypt it. So it goes without saying, you’d have to push the data to a second device which handles decryption.
No
Oh… so how do you decrypt your data without a decryption key? Don’t tell me you use a password…
Do you store your password on the device in cleartext? Thats stupid.
Just no, youre plain wrong.
Obviously not. Do you store your false equivalency fallacies on the internet in clear text? Apparently so, but I won’t call you stupid for it.
Are you telling me, fuck all to the popular mantra that: if they have physical access to device, you’re boned?
State sponsored forensic programs bypass TPM and shit all the time, requiring physical access.
So where is your hypothetical security coming from? To me, it sounds like you’re needlessly giving me a hard time on a subject I probably understand better than you.
Sigh
https://en.wikipedia.org/wiki/One-way_function?wprov=sfla1