Read-only, rootless container with only the cache/transcode/config folders mounted RW+noexec - ideally both with a volume size limit.
Reverse proxy only the absolutely minimal ports needed, with some security measures (e.g. crowdsec transparent proxy, hooked up to both your firewall and reverse proxy to block malicious actors.


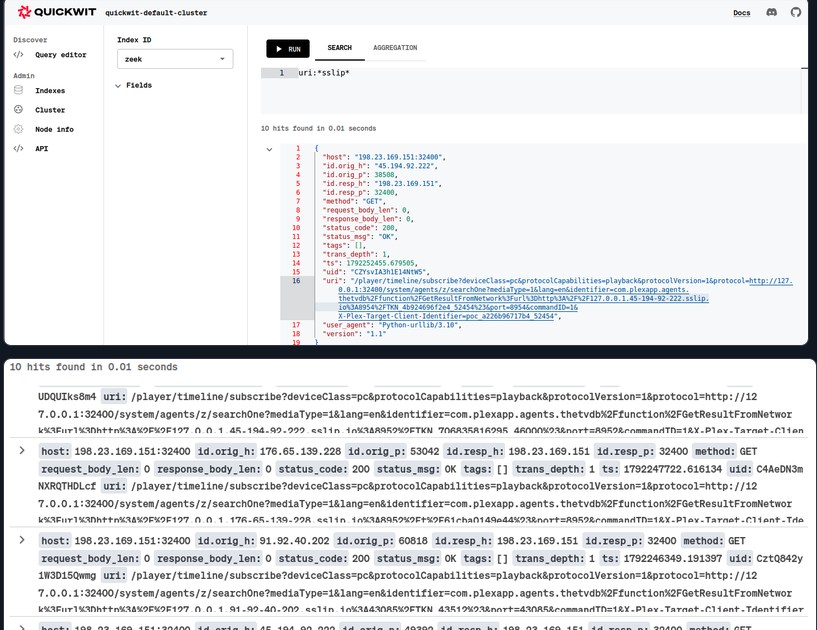
Even without data compromise or pivoting, they can still mine crypto on your hardware, launch a ddos, spam email, do botnet stuff, or host CSAM.
Not if your Jellyfin is set up correctly.
Read-only, rootless container with only the cache/transcode/config folders mounted RW+noexec - ideally both with a volume size limit.
Reverse proxy only the absolutely minimal ports needed, with some security measures (e.g. crowdsec transparent proxy, hooked up to both your firewall and reverse proxy to block malicious actors.