I think people over blow how dangerous it is. Or maybe its better most people dont. I don’t know I know the issues and I take measures to mitigate them. Then if someone gets in they would be limited to vlan. And if somebody gets out of that good wasted so much effort for nothing since I have nothing that would be worth that much trouble.
And before someone says identity pretty sire that has been in so many other leaks overt the years the information is pretty old.
Read-only, rootless container with only the cache/transcode/config folders mounted RW+noexec - ideally both with a volume size limit.
Reverse proxy only the absolutely minimal ports needed, with some security measures (e.g. crowdsec transparent proxy, hooked up to both your firewall and reverse proxy to block malicious actors.


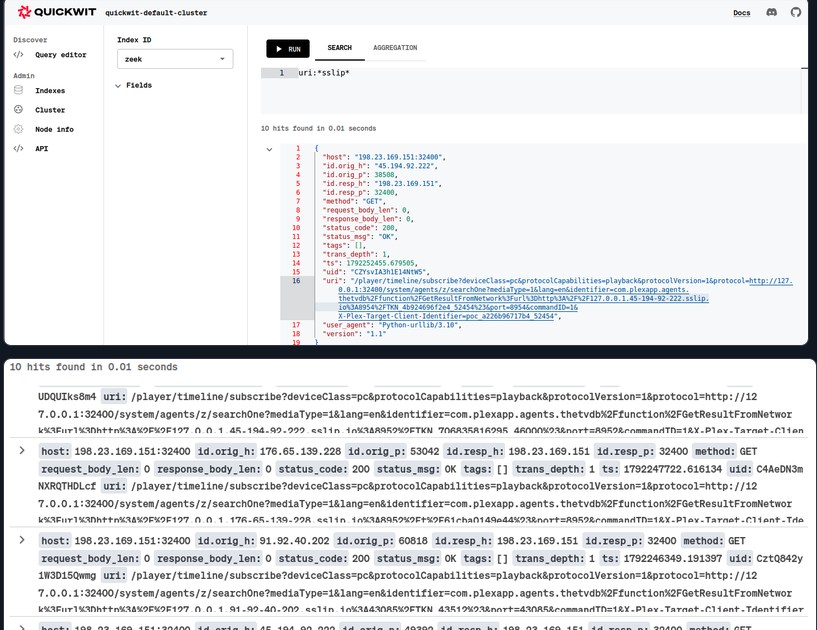
I think people over blow how dangerous it is. Or maybe its better most people dont. I don’t know I know the issues and I take measures to mitigate them. Then if someone gets in they would be limited to vlan. And if somebody gets out of that good wasted so much effort for nothing since I have nothing that would be worth that much trouble.
And before someone says identity pretty sire that has been in so many other leaks overt the years the information is pretty old.
Even without data compromise or pivoting, they can still mine crypto on your hardware, launch a ddos, spam email, do botnet stuff, or host CSAM.
Not if your Jellyfin is set up correctly.
Read-only, rootless container with only the cache/transcode/config folders mounted RW+noexec - ideally both with a volume size limit.
Reverse proxy only the absolutely minimal ports needed, with some security measures (e.g. crowdsec transparent proxy, hooked up to both your firewall and reverse proxy to block malicious actors.