There’s usually nothing wrong with just clicking a link (if your browser is set up correctly). The problem begins if you actually enter any sort of information in a random website or something.
No, you generally should not be worried about that.
Generally the worst thing that a website can get from you just opening a URL is (1) whether or not you’re logged in to google/facebook/etc, (2) your advertisement profile/who you are, (3) roughly where you are. All those are privacy issues, not a security issue, hence not very related to the “cybersecurity course”, and only the first one is tangentially related to being logged in.
You should of course use various anti-tracking measures, e.g. an adblocker, “resist fingerprinting” in Librewolf, user agent faker, a good VPN, etc. That will reduce the exposure to all 3 issues above, but once again those are not security problems.
You should also never download random bullshit to your computer. Having an actual file on disk outside the browser sandbox could indeed be an issue. You could simply forget where it came from and decide to execute it one day, or there could be some bug in some app on your OS which could trigger a code execution exploit.
However, if your browser shares authentication details with random websites like what you are describing, you should stop using it immediately.
This is extremely bad advice and is akin to saying there is nothing wrong with shooting someone in the chest as long as they’re wearing a bulletproof vest.
Sketchy websites should be avoided. Even experts don’t think of everything possible to attack.
It’s the same reason you shouldn’t expose your pc directly to the internet even if you have a secure os installed.
…Bonus points for you in another thread today doubting that it’s possible to lock one’s keys in a car.

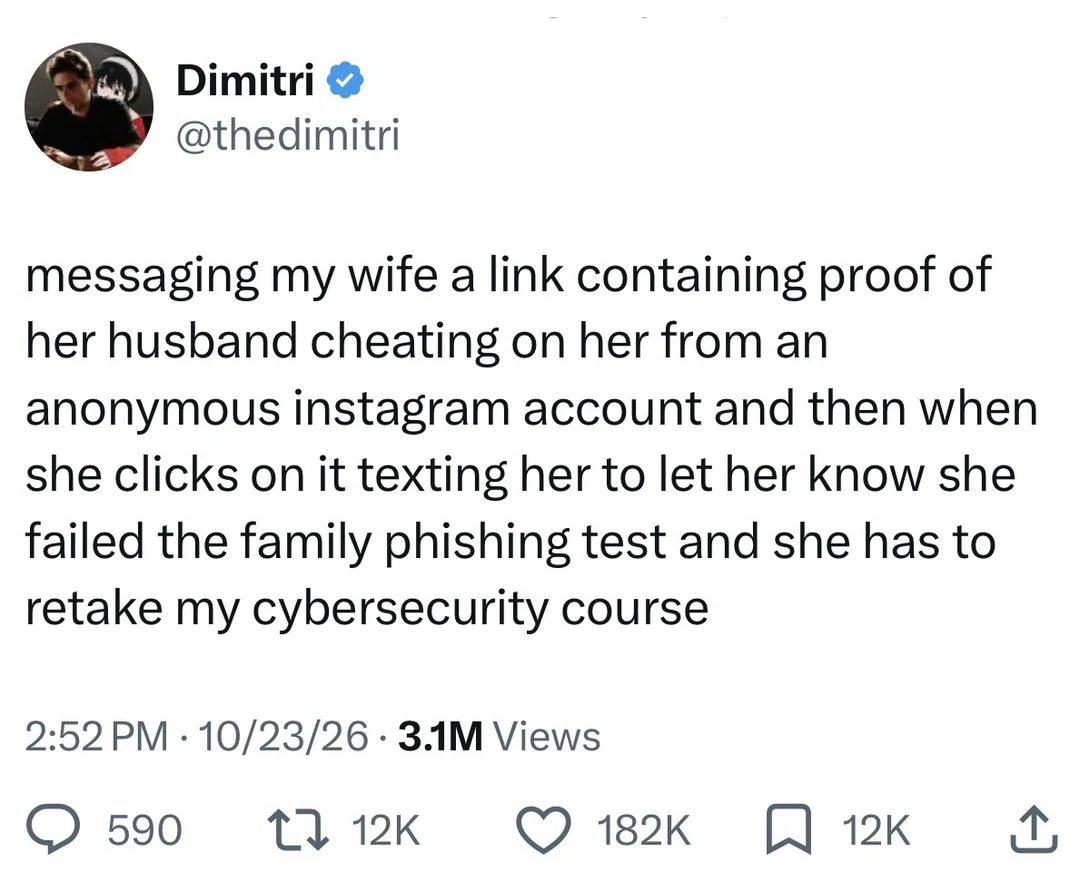
There’s usually nothing wrong with just clicking a link (if your browser is set up correctly). The problem begins if you actually enter any sort of information in a random website or something.
Be extra careful if you’re logged in on any other site in another tab though. Or even if you closed the tab.
No, you generally should not be worried about that.
Generally the worst thing that a website can get from you just opening a URL is (1) whether or not you’re logged in to google/facebook/etc, (2) your advertisement profile/who you are, (3) roughly where you are. All those are privacy issues, not a security issue, hence not very related to the “cybersecurity course”, and only the first one is tangentially related to being logged in.
You should of course use various anti-tracking measures, e.g. an adblocker, “resist fingerprinting” in Librewolf, user agent faker, a good VPN, etc. That will reduce the exposure to all 3 issues above, but once again those are not security problems.
You should also never download random bullshit to your computer. Having an actual file on disk outside the browser sandbox could indeed be an issue. You could simply forget where it came from and decide to execute it one day, or there could be some bug in some app on your OS which could trigger a code execution exploit.
However, if your browser shares authentication details with random websites like what you are describing, you should stop using it immediately.
This is extremely bad advice and is akin to saying there is nothing wrong with shooting someone in the chest as long as they’re wearing a bulletproof vest.
Sketchy websites should be avoided. Even experts don’t think of everything possible to attack.
It’s the same reason you shouldn’t expose your pc directly to the internet even if you have a secure os installed.
…Bonus points for you in another thread today doubting that it’s possible to lock one’s keys in a car.