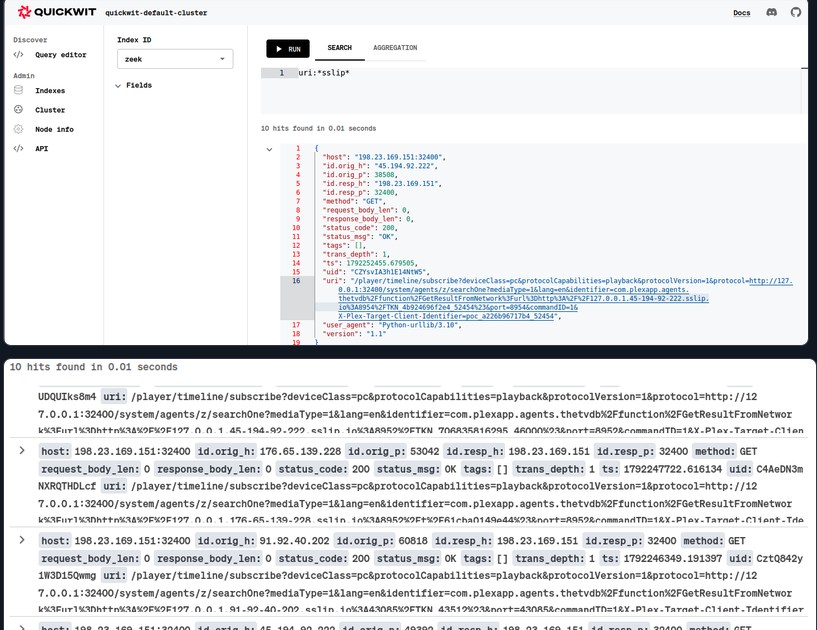
The update got released over 2 months ago. So sensible admins should not be getting hit by this.
Also I use Jellyfin btw.
If you want to expose plex to the open Internet (not a VPN) Don’t open the plex port to the internet. Turn off the “remote access” setting and run it behind a reverse proxy instead.
And if you run a reverse proxy, put crowdsec on it. The free options for filters are pretty well maintained.
Also I use Jellyfin btw.
Oh god, its the new Arch isn’t it…
Everyone talks about Jellyfin, but I just switched to Emby and I couldn’t be happier (no connect cloud stuff). Can someone please let me know why and how I just made the worst decision of my life please.
The main reason is that if you switch from Plex to Emby you’re going from paid licenseware (fully enshittified) to paid licenseware (not fully enshittified yet). It’s like when everyone finally dropped Skype and moved to… Discord. Which hey it’s closed source and owned by venture capital, but it doesn’t suck yet!!! And now in 2026, Discord is what Discord is.
But I haven’t paid anything to Emby (I don’t need the code behind that key) and without cloud, I could continue using this version forever and they can’t enshitify it
IDK why everyone here is in love with Jellyfin when we have Stremio/Nuvio. Jellyfin is a lot of work; with Nuvio all you do is browse like Netflix, and stream. No existing media library required.
Because a lot of us watch things that cant be found easily, or home movies, or prefer to have it readily available at any time.
There are many reasons. Dont assume your use case is the only one.
I’m stoked on my Jellyfin setup, but I’ll check on Stremio again in case I want to recommend it to anyone. Never heard of Nuvio, but at a glance it seems like you have to connect it to a media library.
Nuvio is the same as Stremio except better, because it has more quality of life features (like a “Who’s watching” feature). I only mentioned Stremio because it’s more well-known than Nuvio, but both work the same way. If anyone remembers Popcorn Time, it’s kinda like that.
Yeah I loved popcorn time. I’m looking into Stremio, and I’m already down a rabbit-hole of add-ons, debrid providers, and reading between the lines. Doesn’t seem like anything I can recommend to nontechnical folks.
I think it’s not a widely used phrase yet
It definitely is in this community
I have everything locally and watch on VLC fwiw /s
Nope
Sure explains why Plex was so cagey and uninformative when they emailed everyone to update their servers a couple months back. Not so much as a CVE report or change set.
A vulnerability? No…. 4 of them. And they stack.
As someone who has nearly all internet facing software auto update with watchtower nightly my cortisol is so low
Am not sensible admin. Though I did just run a backup and update. How likely am I FUBAR?
Edit: I run Plex on a dedicated proxmox VM. Theoretically I could nuke it and start over with my Plex database file. Though there’s some config I’d have to do again and I don’t want to
Also I use Jellyfin btw.
You shouldn’t be talking with the amount of hilarious CVEs jellyfin has also had lmao
I don’t understand, though… Your mom has a bunch of unresolved CVEs and we all bang her anyway, so??
Hopefully with a firewall
I got hit by this a couple days ago.
How did you detect and remove it
I’m guessing this requires it be exposed to the Internet. Please stop exposing services to the Internet.
Sir, this is /c/selfhosted.
Kind of defeats the purpose of Plex and Jellyfin.
*defeats your purpose of Plex and Jellyfin
I just want a media server. I have no use case to make it available to the public internet.
That’s pretty much the number one reason people say they won’t move to Jellyfin - the ease of public access.
Even though exposing your shit to Internet is a terrible idea for most people.
I think people over blow how dangerous it is. Or maybe its better most people dont. I don’t know I know the issues and I take measures to mitigate them. Then if someone gets in they would be limited to vlan. And if somebody gets out of that good wasted so much effort for nothing since I have nothing that would be worth that much trouble.
And before someone says identity pretty sire that has been in so many other leaks overt the years the information is pretty old.
Even without data compromise or pivoting, they can still mine crypto on your hardware, launch a ddos, spam email, do botnet stuff, or host CSAM.
Not if your Jellyfin is set up correctly.
Read-only, rootless container with only the cache/transcode/config folders mounted RW+noexec - ideally both with a volume size limit.
Reverse proxy only the absolutely minimal ports needed, with some security measures (e.g. crowdsec transparent proxy, hooked up to both your firewall and reverse proxy to block malicious actors.