
I gotta do this.
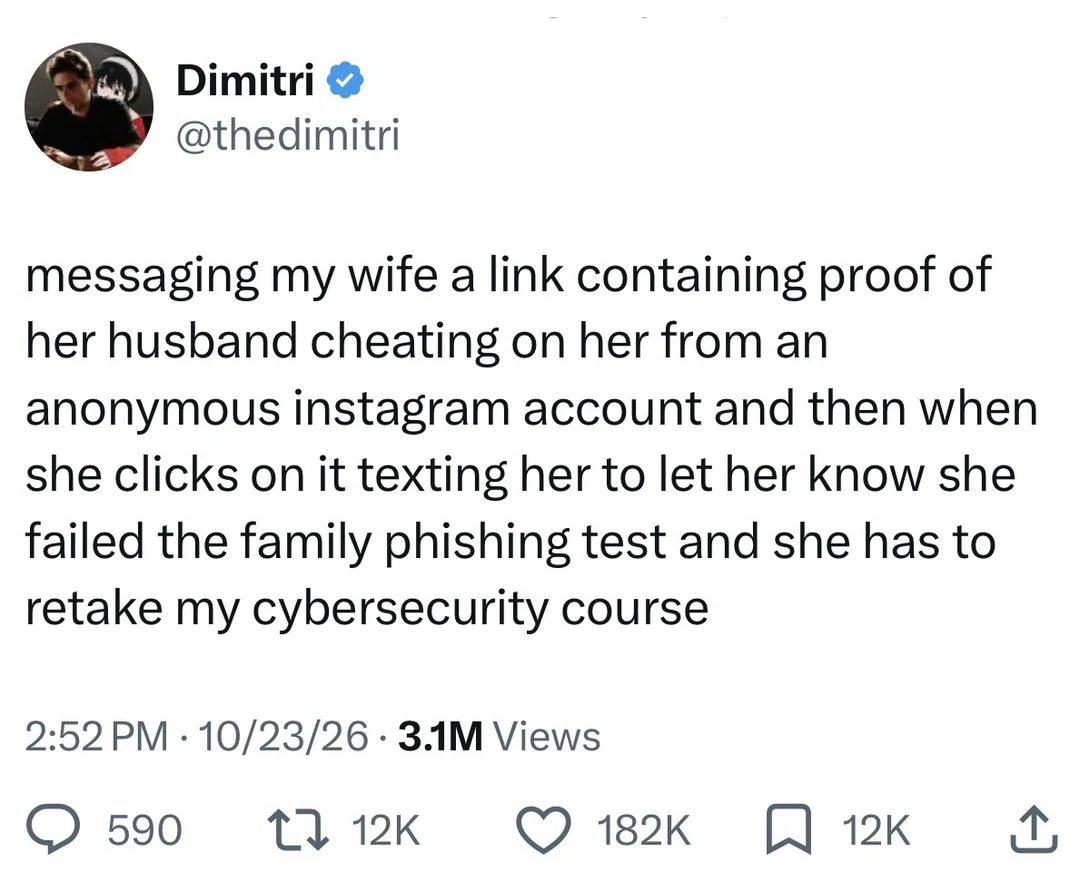
It’s a honey pot of a different color! Genius!
You have chosen Death by chancla
His wife is not Italian. If she was he would not even dare to do anything of the sort.
All these people setting up filters don’t understand it is supposed to train you in case a real phishing attempt is made.
Those filters aren’t going to stop real ones.
But if you want to blow up the database server you need to work on because you couldn’t be bothered to click a button when a phishing test comes around, then you better quit your job in tech.
I swear, developers are some of the biggest security concerns in any company. They complain the moment some access is blocked for good reason. Much bigger concern than old nancy “never-had-a-computer-at-home” clicks-a-lot.
If the fake phishing emails can be caught by my very rudimentary filter they weren’t particularly good anyway. Besides, I still have to look at those emails and report them, otherwise my IT still counts it as a strike against me. Win-win. IT continues to keep me on my toes and I don’t have to take another 30min training course because I ignored an email for a day or two.
Sounds kinda like the Tale of Foolish Curiosity from Don Quixote. Spoiler: the wife was a good woman and wouldn’t have cheated on the guy… until he started being an asshole by subjecting her to endless tests to prove her virtue.
I’ve been meaning to read Don Quixote and this is the tipping point. I want to make quixotic references.
Just read this to a beautiful woman I know.
Her response: That’s not going to end near as well/funny as you think/hope it will.
Neither is your future if your wife maintains such easily exploited vulnerabilities.
Blink 8 times if you’re in danger
Blink 182 times if it’s just all the small things
Did they make a song about that?
If not in danger, just take off your pants and jacket.
And your boots and your sunglasses…geev dem toa meeh.
— Arnold Schwarzenegger as The Terminator
Den get to da choppah
My knee jerk reaction is to calmly explain why this isn’t appropriate in a corporate environment.
I’m so broken.
I saw one with a bunch of maga triggers. The Democrats are doing what!? 😱 they click every time.
May their PCs be infected and their accounts be emptied.
I use dried/powdered abortion to slip into my antifa uniform.
Make sure not to get any gender fluid in there too, or the resulting paste makes removal very difficult
My work email is a .edu, and so most of ours are just social media phishing attempts with fake IG and Tiktok links. But why I’m the world would you use .edu for those?
You wanna target .edu, do a quick check on our publicly accessible faculty pages and pretend to be us. I swear, we’ve got like zero protection against that, lol.
Hey Barb, I forgot my keys, please leave the garage open. Thanks, Jeff.
Boom, stole the faculty coffee maker.
You can probably fence that for more than the $300,000 spectrometer.
You are my world, even if voice to text used to work before AI, but fucks up the simplest shit now.
I’ve set my last name in caps. So any IT Phishing script using a <placeholder lastname> just sends my name in caps. And then I just set up a filter.
They should really try and make them more believable
So what do you do when you get an actual phishing mail that doesn’t type your name in all caps?
Haven’t had one in 4 years. I don’t email to outside. If I would get one I would mark it as such, but I’m not popular enough.
Hello Jelle WHO, You’re no gonna believe it! We’re having issues delivering your packaged extended warranty which claims that your social security bananafits will expire unless you take immediate action. Click this link to know more on how to win big with crypto.
Lol@ “bananafits”
There’s usually nothing wrong with just clicking a link (if your browser is set up correctly). The problem begins if you actually enter any sort of information in a random website or something.
Be extra careful if you’re logged in on any other site in another tab though. Or even if you closed the tab.
No, you generally should not be worried about that.
Generally the worst thing that a website can get from you just opening a URL is (1) whether or not you’re logged in to google/facebook/etc, (2) your advertisement profile/who you are, (3) roughly where you are. All those are privacy issues, not a security issue, hence not very related to the “cybersecurity course”, and only the first one is tangentially related to being logged in.
You should of course use various anti-tracking measures, e.g. an adblocker, “resist fingerprinting” in Librewolf, user agent faker, a good VPN, etc. That will reduce the exposure to all 3 issues above, but once again those are not security problems.
You should also never download random bullshit to your computer. Having an actual file on disk outside the browser sandbox could indeed be an issue. You could simply forget where it came from and decide to execute it one day, or there could be some bug in some app on your OS which could trigger a code execution exploit.
However, if your browser shares authentication details with random websites like what you are describing, you should stop using it immediately.
This is extremely bad advice and is akin to saying there is nothing wrong with shooting someone in the chest as long as they’re wearing a bulletproof vest.
Sketchy websites should be avoided. Even experts don’t think of everything possible to attack.
It’s the same reason you shouldn’t expose your pc directly to the internet even if you have a secure os installed.
…Bonus points for you in another thread today doubting that it’s possible to lock one’s keys in a car.
Is his wife Yor from Spy x Family? While good choice, she’s fictional, so you’re up to the greatest cuckoldry ever witnessed in human history: waifuism.
Unexpected YouTube drama reference